Migrating Banking Workloads to Google Cloud from Replatforming to Reengineering
Architectural analysis of GCP migration patterns for banking workloads, evaluating trade-offs between Rehost, Replatform, and cloud-native Re-engineering.
Relational Database Modernization on Google Cloud: AlloyDB vs Cloud SQL on Zero RPO, Disaggregated Storage, and DORA
Comparative architectural analysis between AlloyDB and Cloud SQL for enterprise mission-critical workloads: disaggregated storage, resilience, and DORA compliance.
GKE Workload Identity Federation with Direct Principal Grants without Intermediate Service Accounts
Advanced IAM architecture for GKE: evolving from intermediate Google Service Account double-hops to Direct Principal Grants for heightened security and DORA auditability.
Market FinOps Platforms vs Custom Tooling: The Reality of Build vs Buy in the Enterprise
Evaluating Build vs Buy in enterprise FinOps. Why market platforms like Apptio and Flexera outperform custom billing data lakes in TCO, FOCUS, and compliance.
Immutable Infrastructure on AWS with Packer, Auto Scaling, and CodeDeploy
Enterprise architectural guide to immutable infrastructure on AWS with Packer Golden and Silver AMIs, EFS storage, and zero-drift replacement patching.
End-to-End Post-Provisioning Automation and Continuous CIS Hardening with Ansible Automation Platform
Orchestrating cloud VM baselines with Ansible Automation Platform: multi-CSP autodiscovery, security agent deployment, and continuous CIS compliance.
Decoupling Platform Governance and Application Delivery with Config Sync and Argo CD on GKE
Dual-engine GitOps architecture pattern for enterprise GKE clusters delegating cluster-wide administration to Anthos Config Sync and application lifecycles to Argo CD.
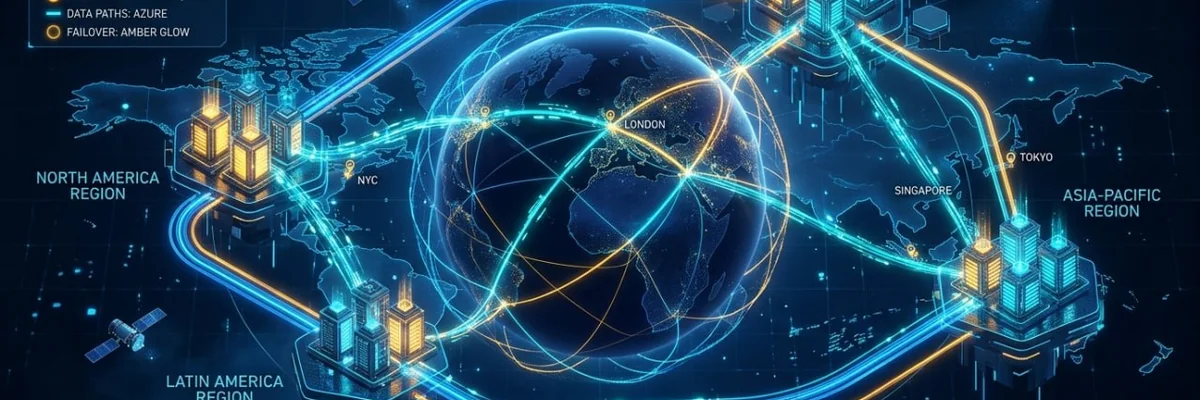
Resilient Cloud Architectures and Multi-Region Strategies for the Financial Sector
Architectural patterns to ensure zero RPO and sub-minute RTO for critical banking workloads: distributed data replication, global health routing, and DORA compliance.
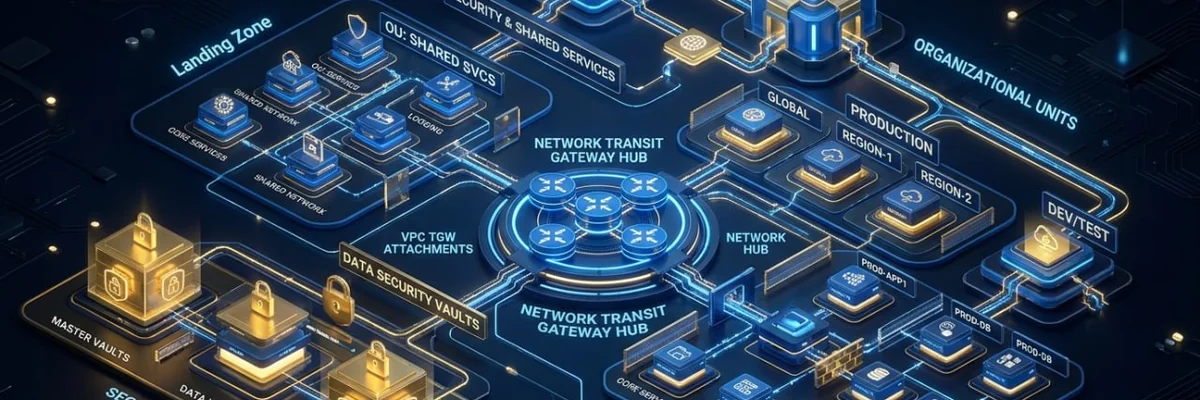
Designing Multi-Account Enterprise Landing Zones for Banking Groups
Architectural patterns for structuring OUs, account vending machines, and Service Control Policies in banking environments compliant with EBA and DORA guidelines.
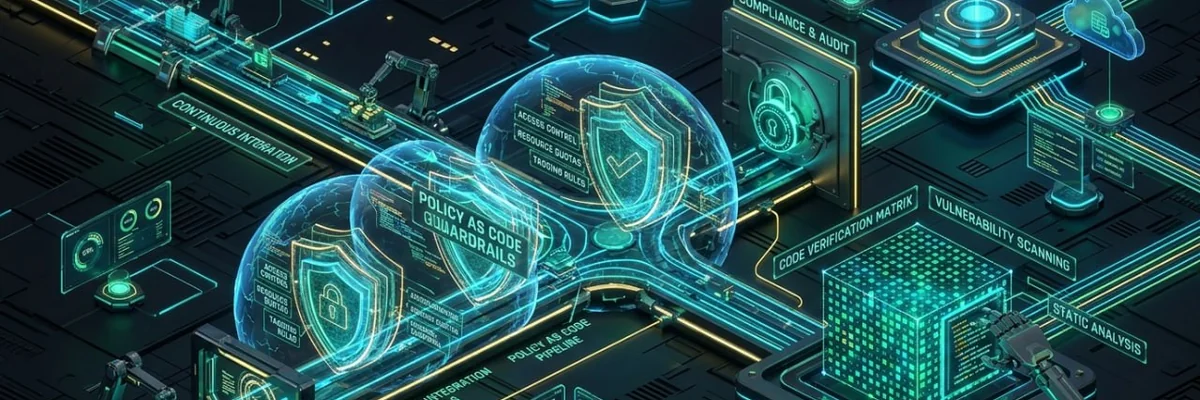
Preventive Guardrails and Policy as Code for Enterprise Cloud Governance
Implementing preventive and reactive controls across multi-cloud landing zones using Open Policy Agent, AWS Control Tower, and Terraform Enterprise to prevent compliance drift.
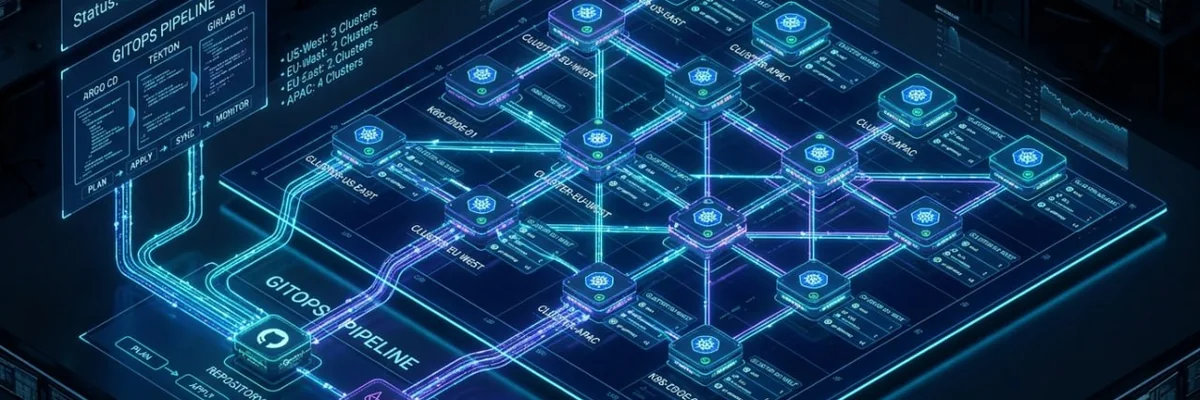
Multi-Cluster Multi-Tenant Governance with Argo CD ApplicationSet and Matrix Generator
Advanced strategies for scaling declarative deployments across dozens of isolated clusters, separating infrastructure governance from application development teams.
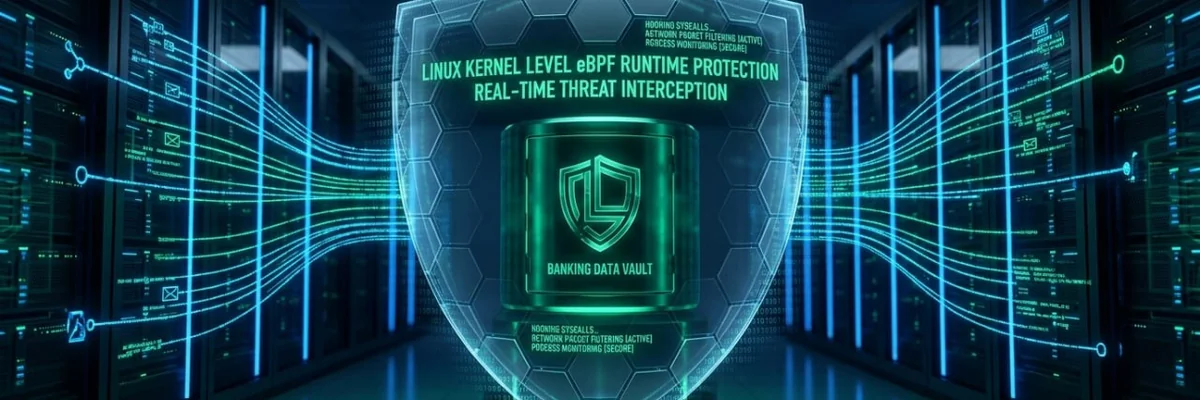
Cilium Tetragon vs Falco for Runtime Security in Banking Environments
Architectural comparison between eBPF kprobes and tracepoints for threat detection in enterprise Kubernetes clusters: active runtime prevention and DORA compliance.
Confidential Computing on Public Cloud for Critical Financial Workloads
Protecting in-use data through hardware-based memory encryption with AMD SEV-SNP and Intel TDX in payment pipelines and remote cryptographic attestation.
Advanced GPU Allocation Patterns with Kubernetes Dynamic Resource Allocation
Overcoming the Kubernetes Device Plugin model: how to allocate heterogeneous GPUs and accelerators on-demand via Structured Parameters, reducing FinOps overhead in enterprise AI clusters.
OpenTelemetry Collector as the Backbone of Enterprise Observability on Multi-Cluster Kubernetes
Consolidating traces, metrics, and logs into a single pipeline reduces operational debt at scale, but requires careful governance of Semantic Conventions and time series cardinality.
Enterprise Architecture and FinOps Optimization with Istio Ambient Mesh
Transitioning to a sidecarless service mesh scales the proxy layer natively in high-density banking clusters and eliminates latent computational overhead.
Security Architectures for Agentic AI in the Banking Sector
The evolution from chatbots to intelligent agents requires new governance paradigms based on sandboxing, just-in-time privileges, and immutable tracking of reasoning chains.
Zero Trust Architecture for Kubernetes with External Secrets Operator and Vault
How the integration between External Secrets Operator and HashiCorp Vault enables cryptographic segregation and centralized auditing in multi-tenant clusters.
Kafka Becomes a Message Broker with KIP-932 Queue Semantics in GA
With Apache Kafka 4.2 and the general availability of Queues for Kafka, the boundary between event streaming and queueing disappears, transforming the architecture of enterprise messaging systems.
Seamless Migration from Ingress NGINX
Translating Ingress NGINX to Gateway API is not a mechanical refactor, as some implicit behaviors change semantics and can cause silent outages.
Oracle Cloud Architectures for Regulated Banks
Technical analysis of architectural choices on Oracle Cloud in high-scale and compliance banking contexts.
Architecture and Challenges in Large-Scale Virtual Machine Migration to the Enterprise Cloud
Analysis of network patterns and replication strategies to orchestrate the rehosting of legacy workloads in high-density banking contexts.
IaC Governance in Regulated Environments with OpenTofu and Native State Encryption
With OpenTofu 1.12 and client-side state encryption via KMS, the choice between OpenTofu and Terraform post-IBM becomes a long-term governance decision, not just a licensing issue.
The Enterprise Path for AI Inference on Kubernetes After WG Serving
The conclusion of the Kubernetes Serving Working Group marks the maturity of the cluster as an AI inference platform and defines the reference stack for enterprise environments.
Intelligent Agents Connected to Databases with Model Context Protocol on Google Cloud
Google extends MCP support to six database services, enabling AI agents to interact directly with enterprise data without infrastructural overhead.
Cilium 1.19 Strict Mode Encryption and Zero Trust for Enterprise Kubernetes
Cilium 1.19 brings inter-node encryption in strict mode, beta integration with Ztunnel for sidecar-less mTLS, and critical observability improvements for large clusters.
GKE Inference Gateway: Intelligent Routing for LLMs in Production
How GKE Inference Gateway reduces Time to First Token (TTFT) latency by 35% and halves P95 for mixed AI workloads, with direct implications for enterprise teams in regulated environments.
How I Built and Automated This Website
A technical deep dive behind the scenes of my personal website. Architecture, security, and automation with Raspberry Pi, Nginx, Let's Encrypt, and Fail2Ban.
Welcome to my Blog: Cloud Architecture, Resilience, and Modernization
The manifesto of Carlo Cruciani's technical blog. Architectural vision, enterprise resilience, Kubernetes, FinOps, and modern distributed systems governance.